Personal infrastructure
Run a certificate server for one owner's devices and manage access independently.
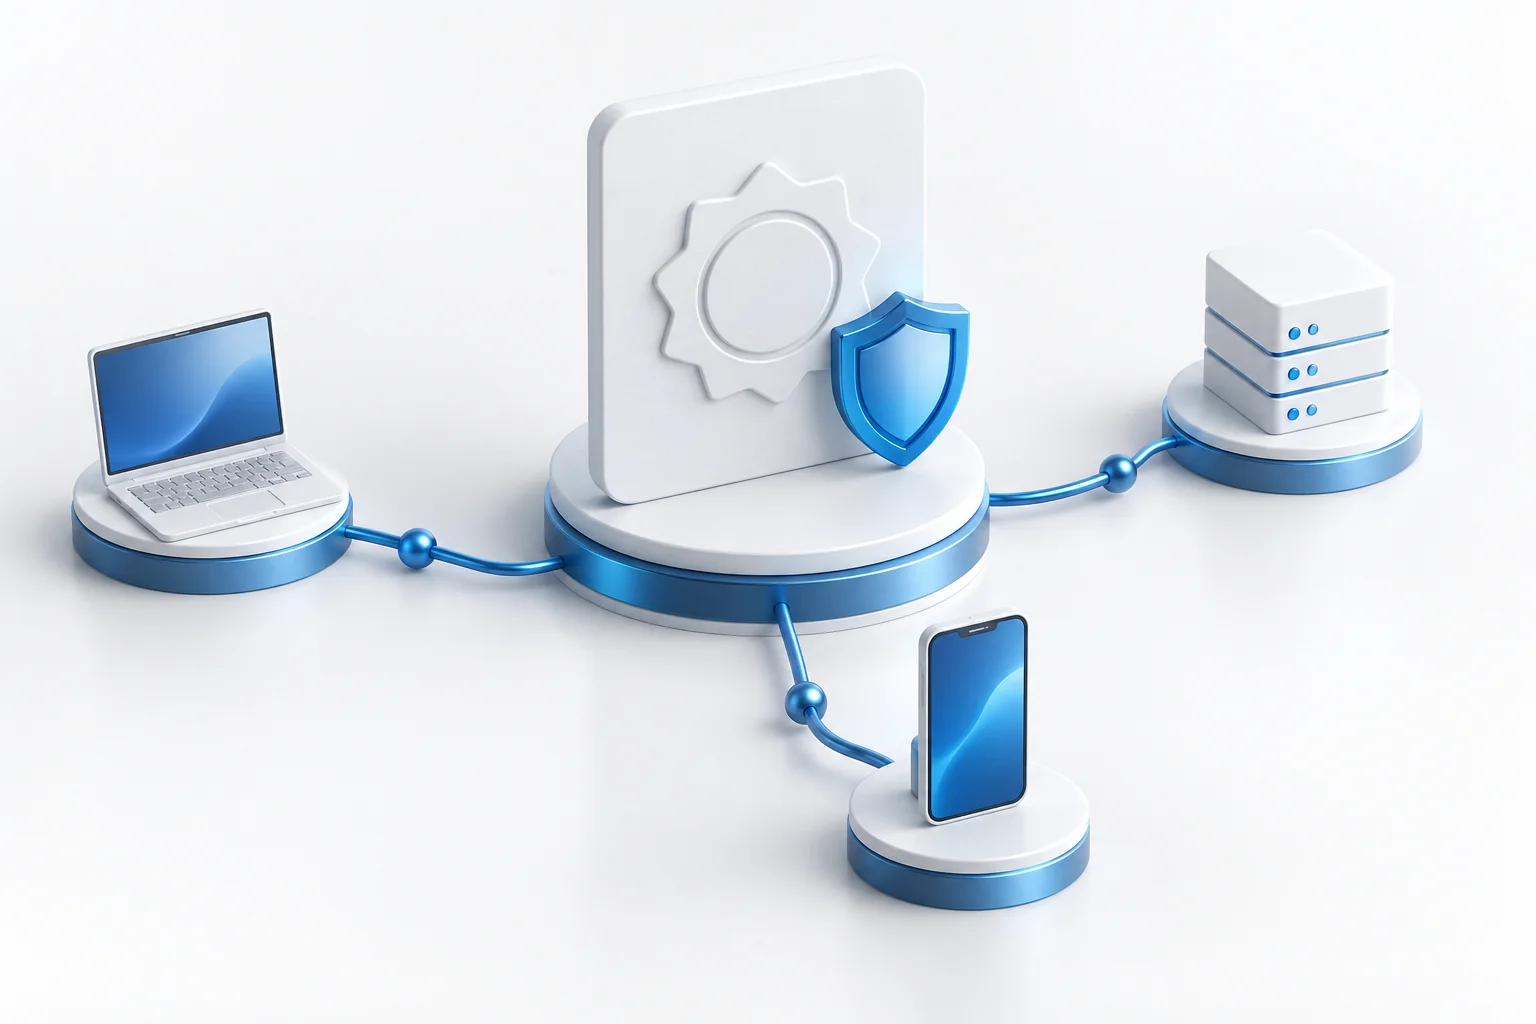
When different devices and people connect to a network, a server address alone is not enough. You need to know who is on the other end and what they are allowed to do. ARCnet Identity is being developed as the platform's certificate service, verifying device identities and helping manage access permissions. Owners can choose a service to trust or run their own for their infrastructure.
Planned · This page describes the intended model. A public release has not been announced; available features and supported devices will be clarified as development progresses.
A device name helps a person recognise it; a certificate supports checking its identity when it interacts with other parts of the platform. Identity provides this foundation for trust. It helps distinguish a known device from an outsider presenting a similar name or appearing at a familiar address.
Networks change: devices are added, older equipment is retired and access may no longer be needed. Certification must cover this lifecycle, including issuing and revoking certificates. A certificate does not mean unrestricted authority: a participant's identity and the actions they may perform are separate questions.
The certificate server may belong to your private infrastructure or a service you have chosen to work with. Running your own lets you organise network maintenance yourself. ARCnet Directory will help you find an option or start deploying your own, but a directory listing is not automatic grounds for trust.
A Supervisor maintains devices connected to one certificate server. Choosing an Identity service is therefore also related to how technical support will be organised. An owner may handle that role in a private network; an organisation may assign maintenance to an administrator or support team.
Before choosing a server, consider who will add devices, maintain them and recover access if a phone is lost. A guide to deployment and common certificate operations is planned for the public release. This information will help you organise network maintenance and assign responsibility for it.
Run a certificate server for one owner's devices and manage access independently.
Provide a common basis of trust for work devices and clear responsibility for their maintenance.
Consider certification and support options, then make an informed choice for your network.